WireGuard by default
Modern peer-based VPN architecture with per-device keys and isolated addresses.
Modern peer-based VPN architecture with per-device keys and isolated addresses.
Use a shared public egress address or reserve a dedicated address where available.
Separate limits allow predictable service tiers instead of one generic bandwidth cap.
Per-device and per-service counters make consumption visible to both admins and customers.
Each service can support one or many independently managed peers depending on the plan.
WHMCS provisioning, suspension, reactivation, termination and trial expiry are synchronized with the VPN control plane.
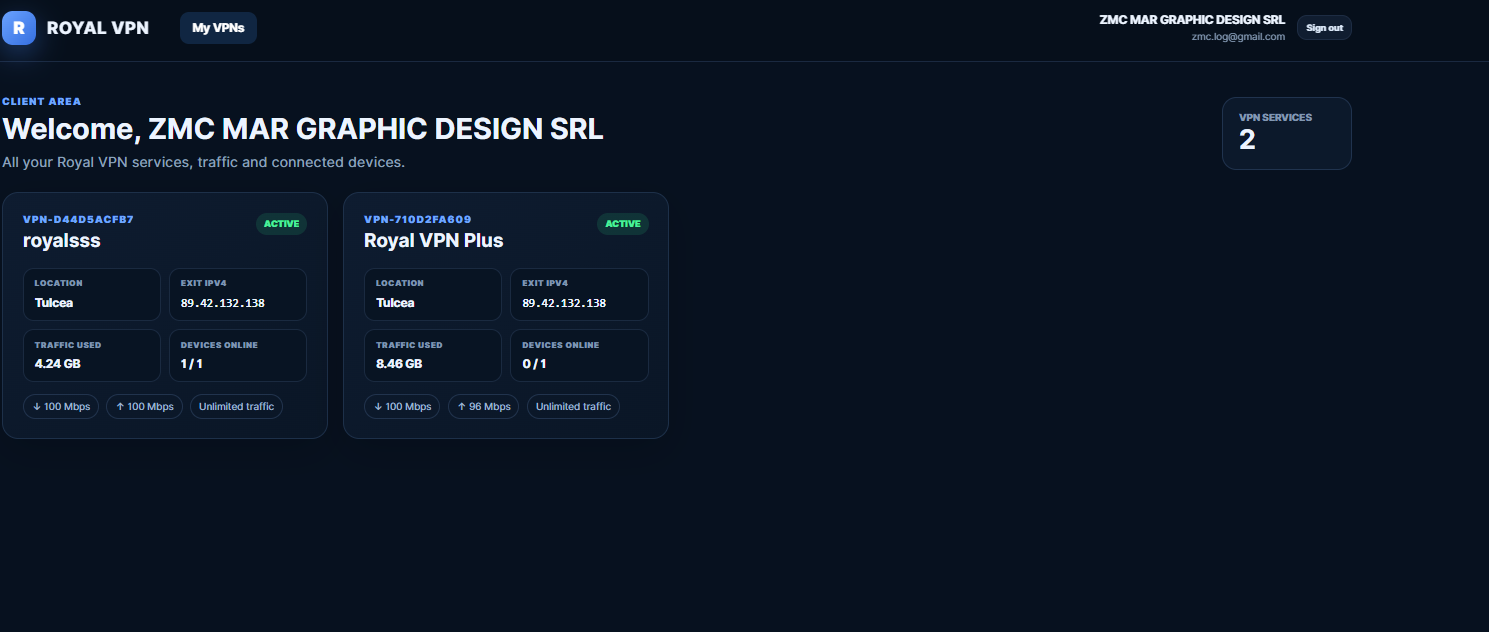
Customers can see multiple VPN subscriptions, online devices, traffic consumption and speed limits from the same account.